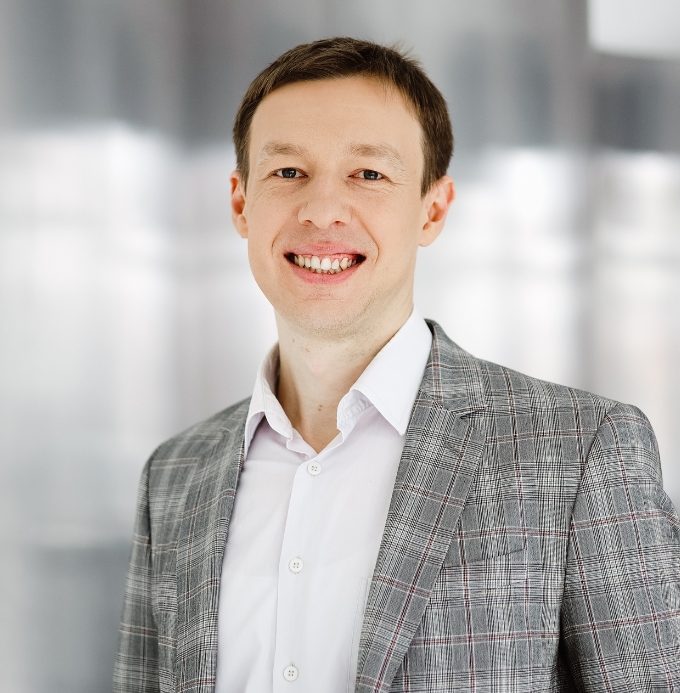
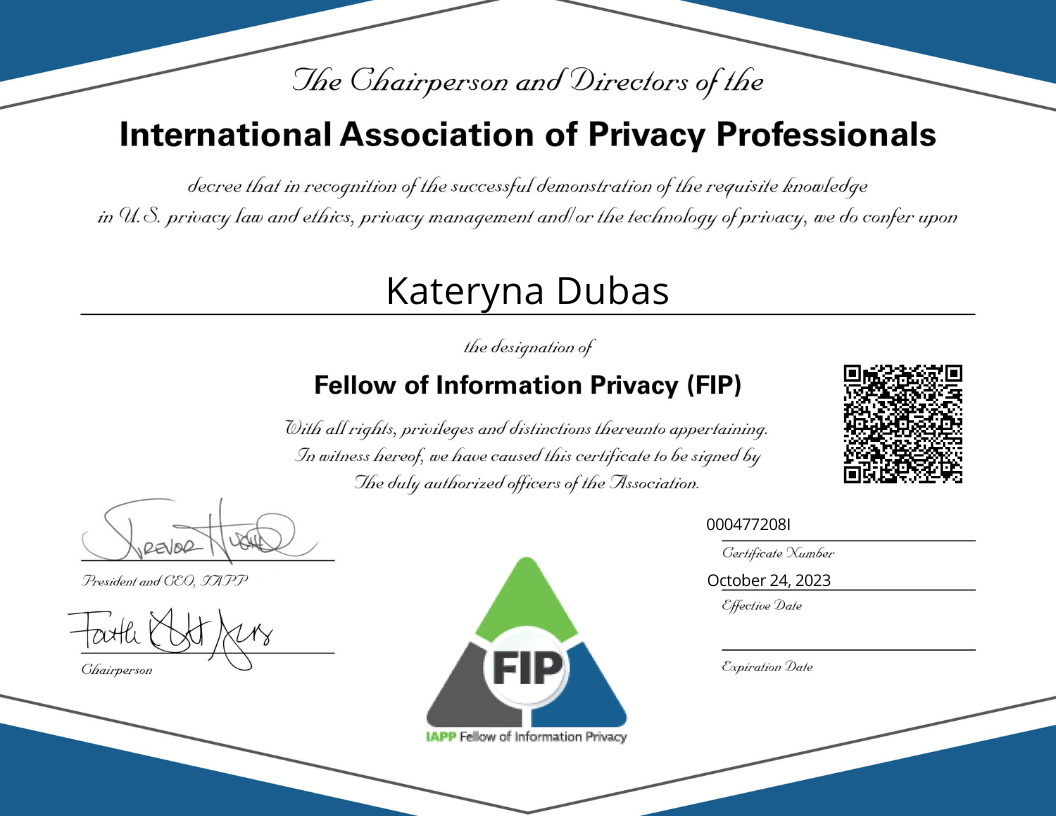
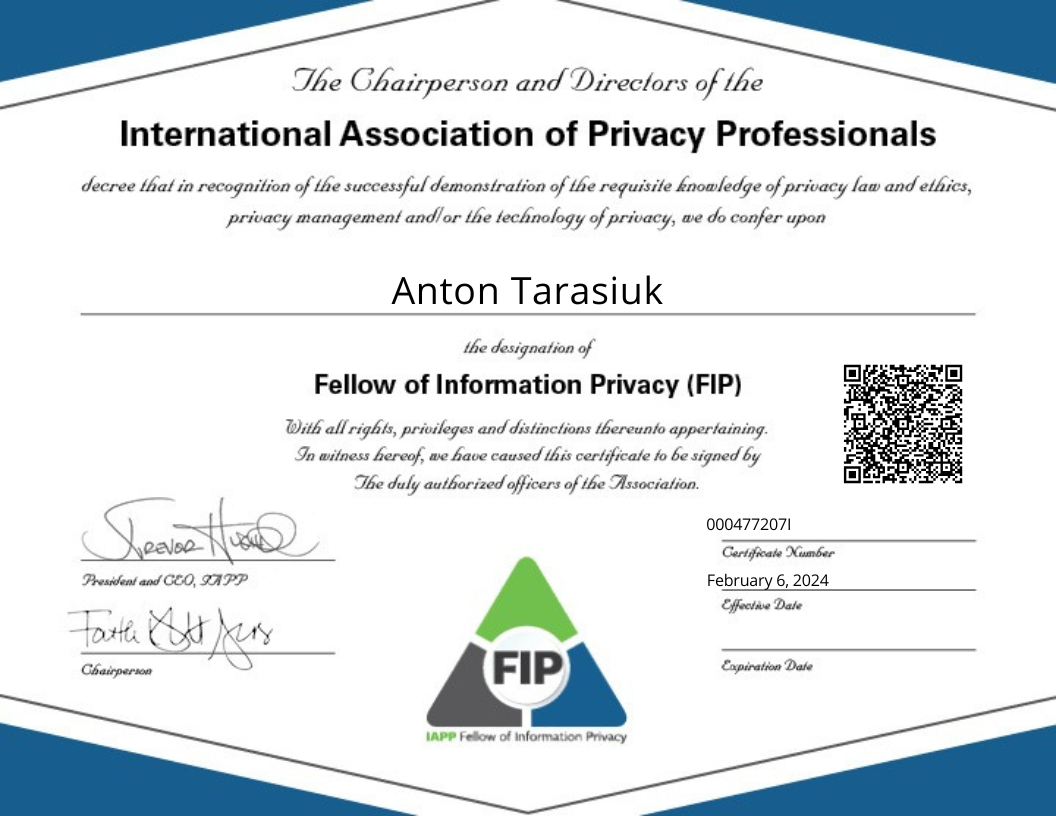
A team of three FIPs
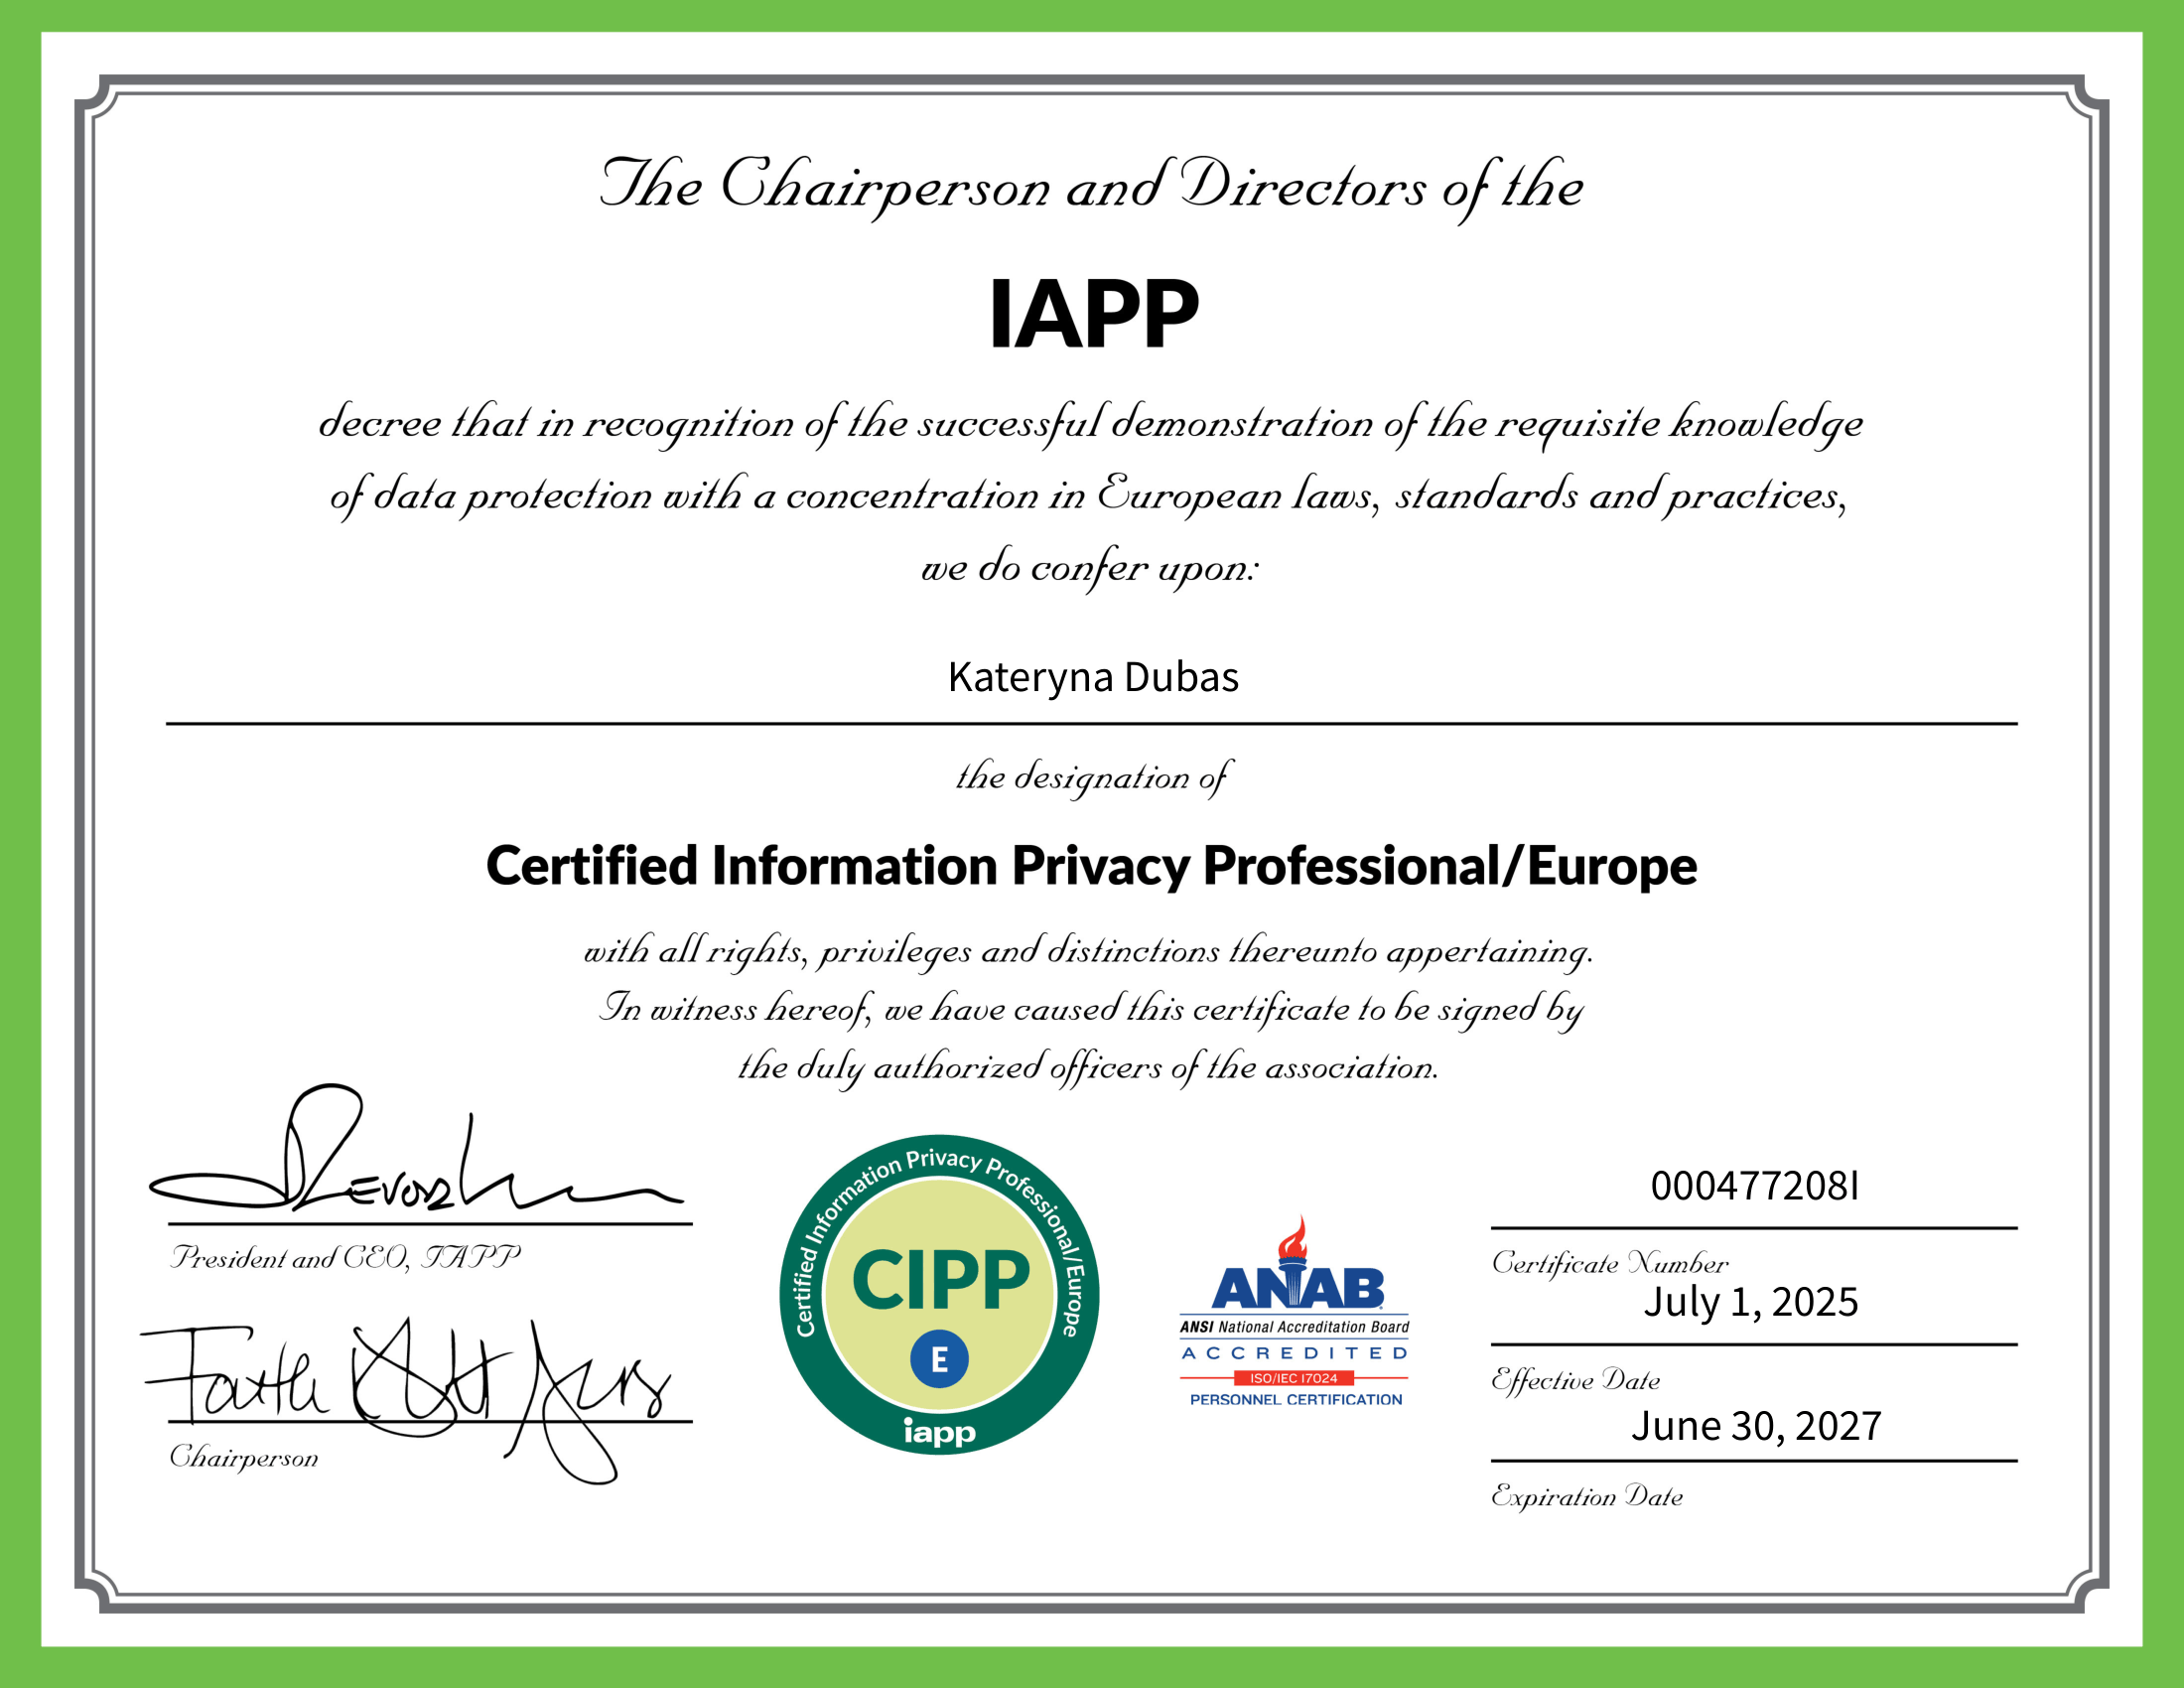
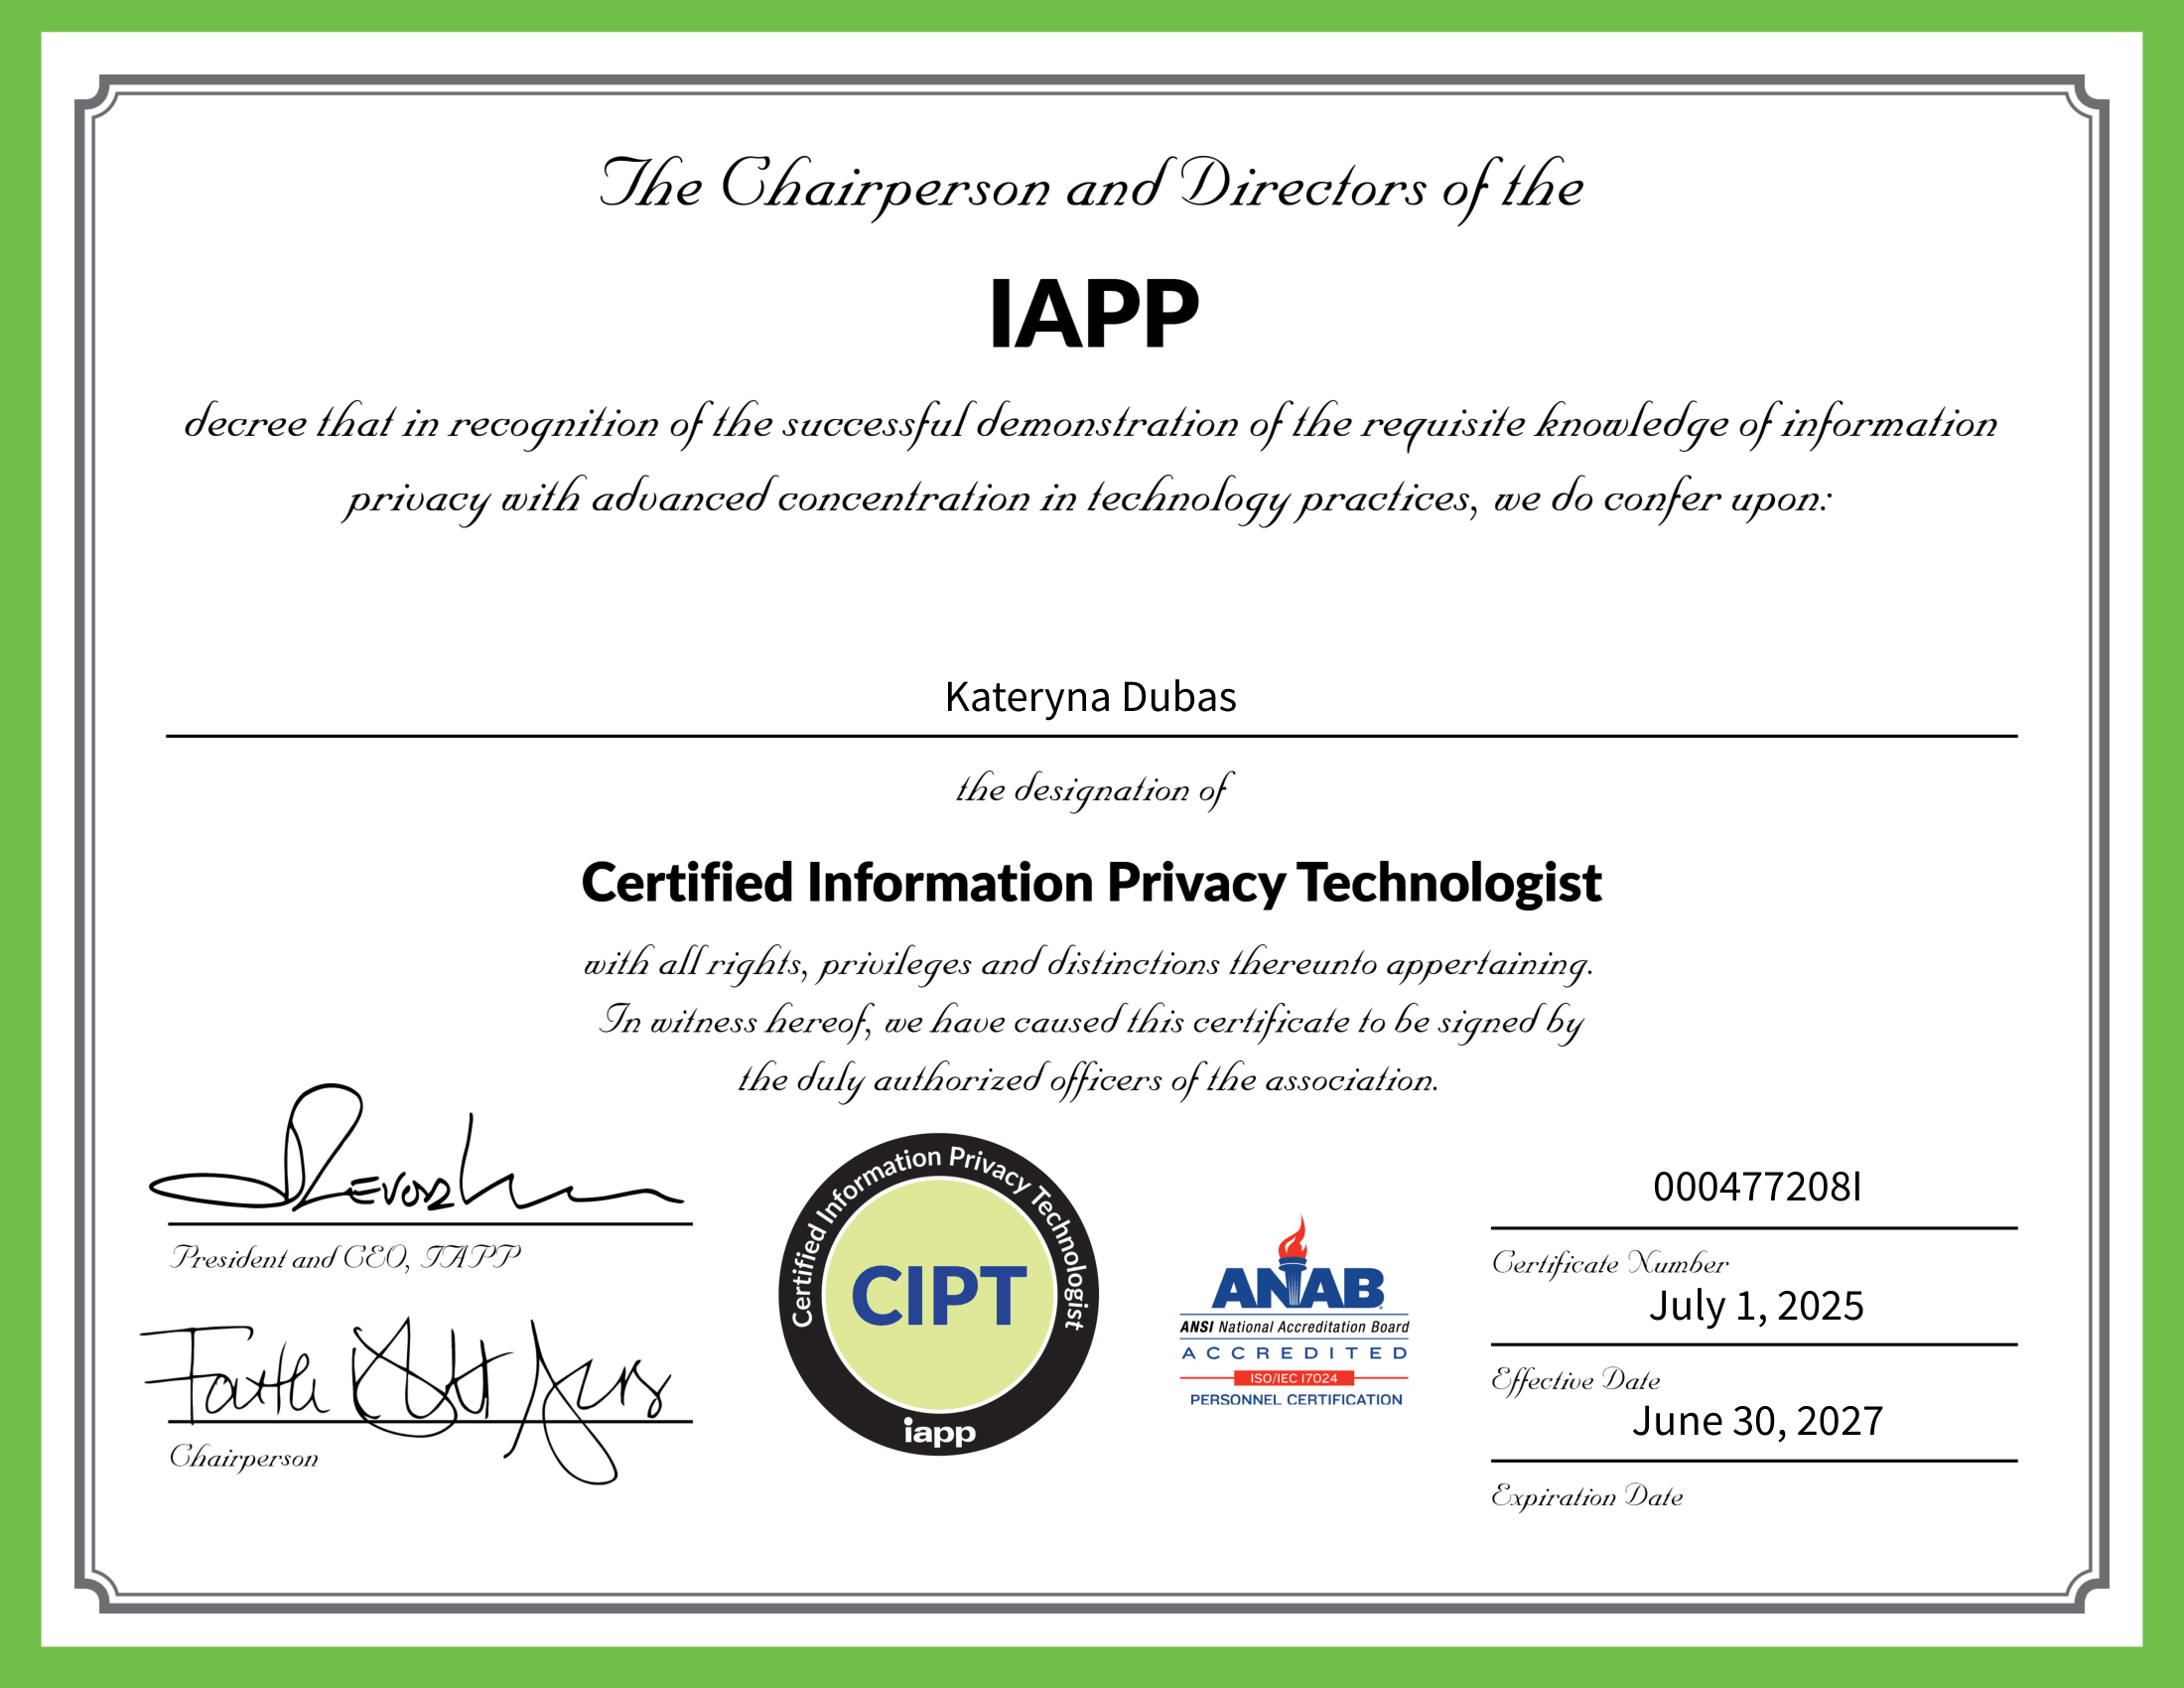
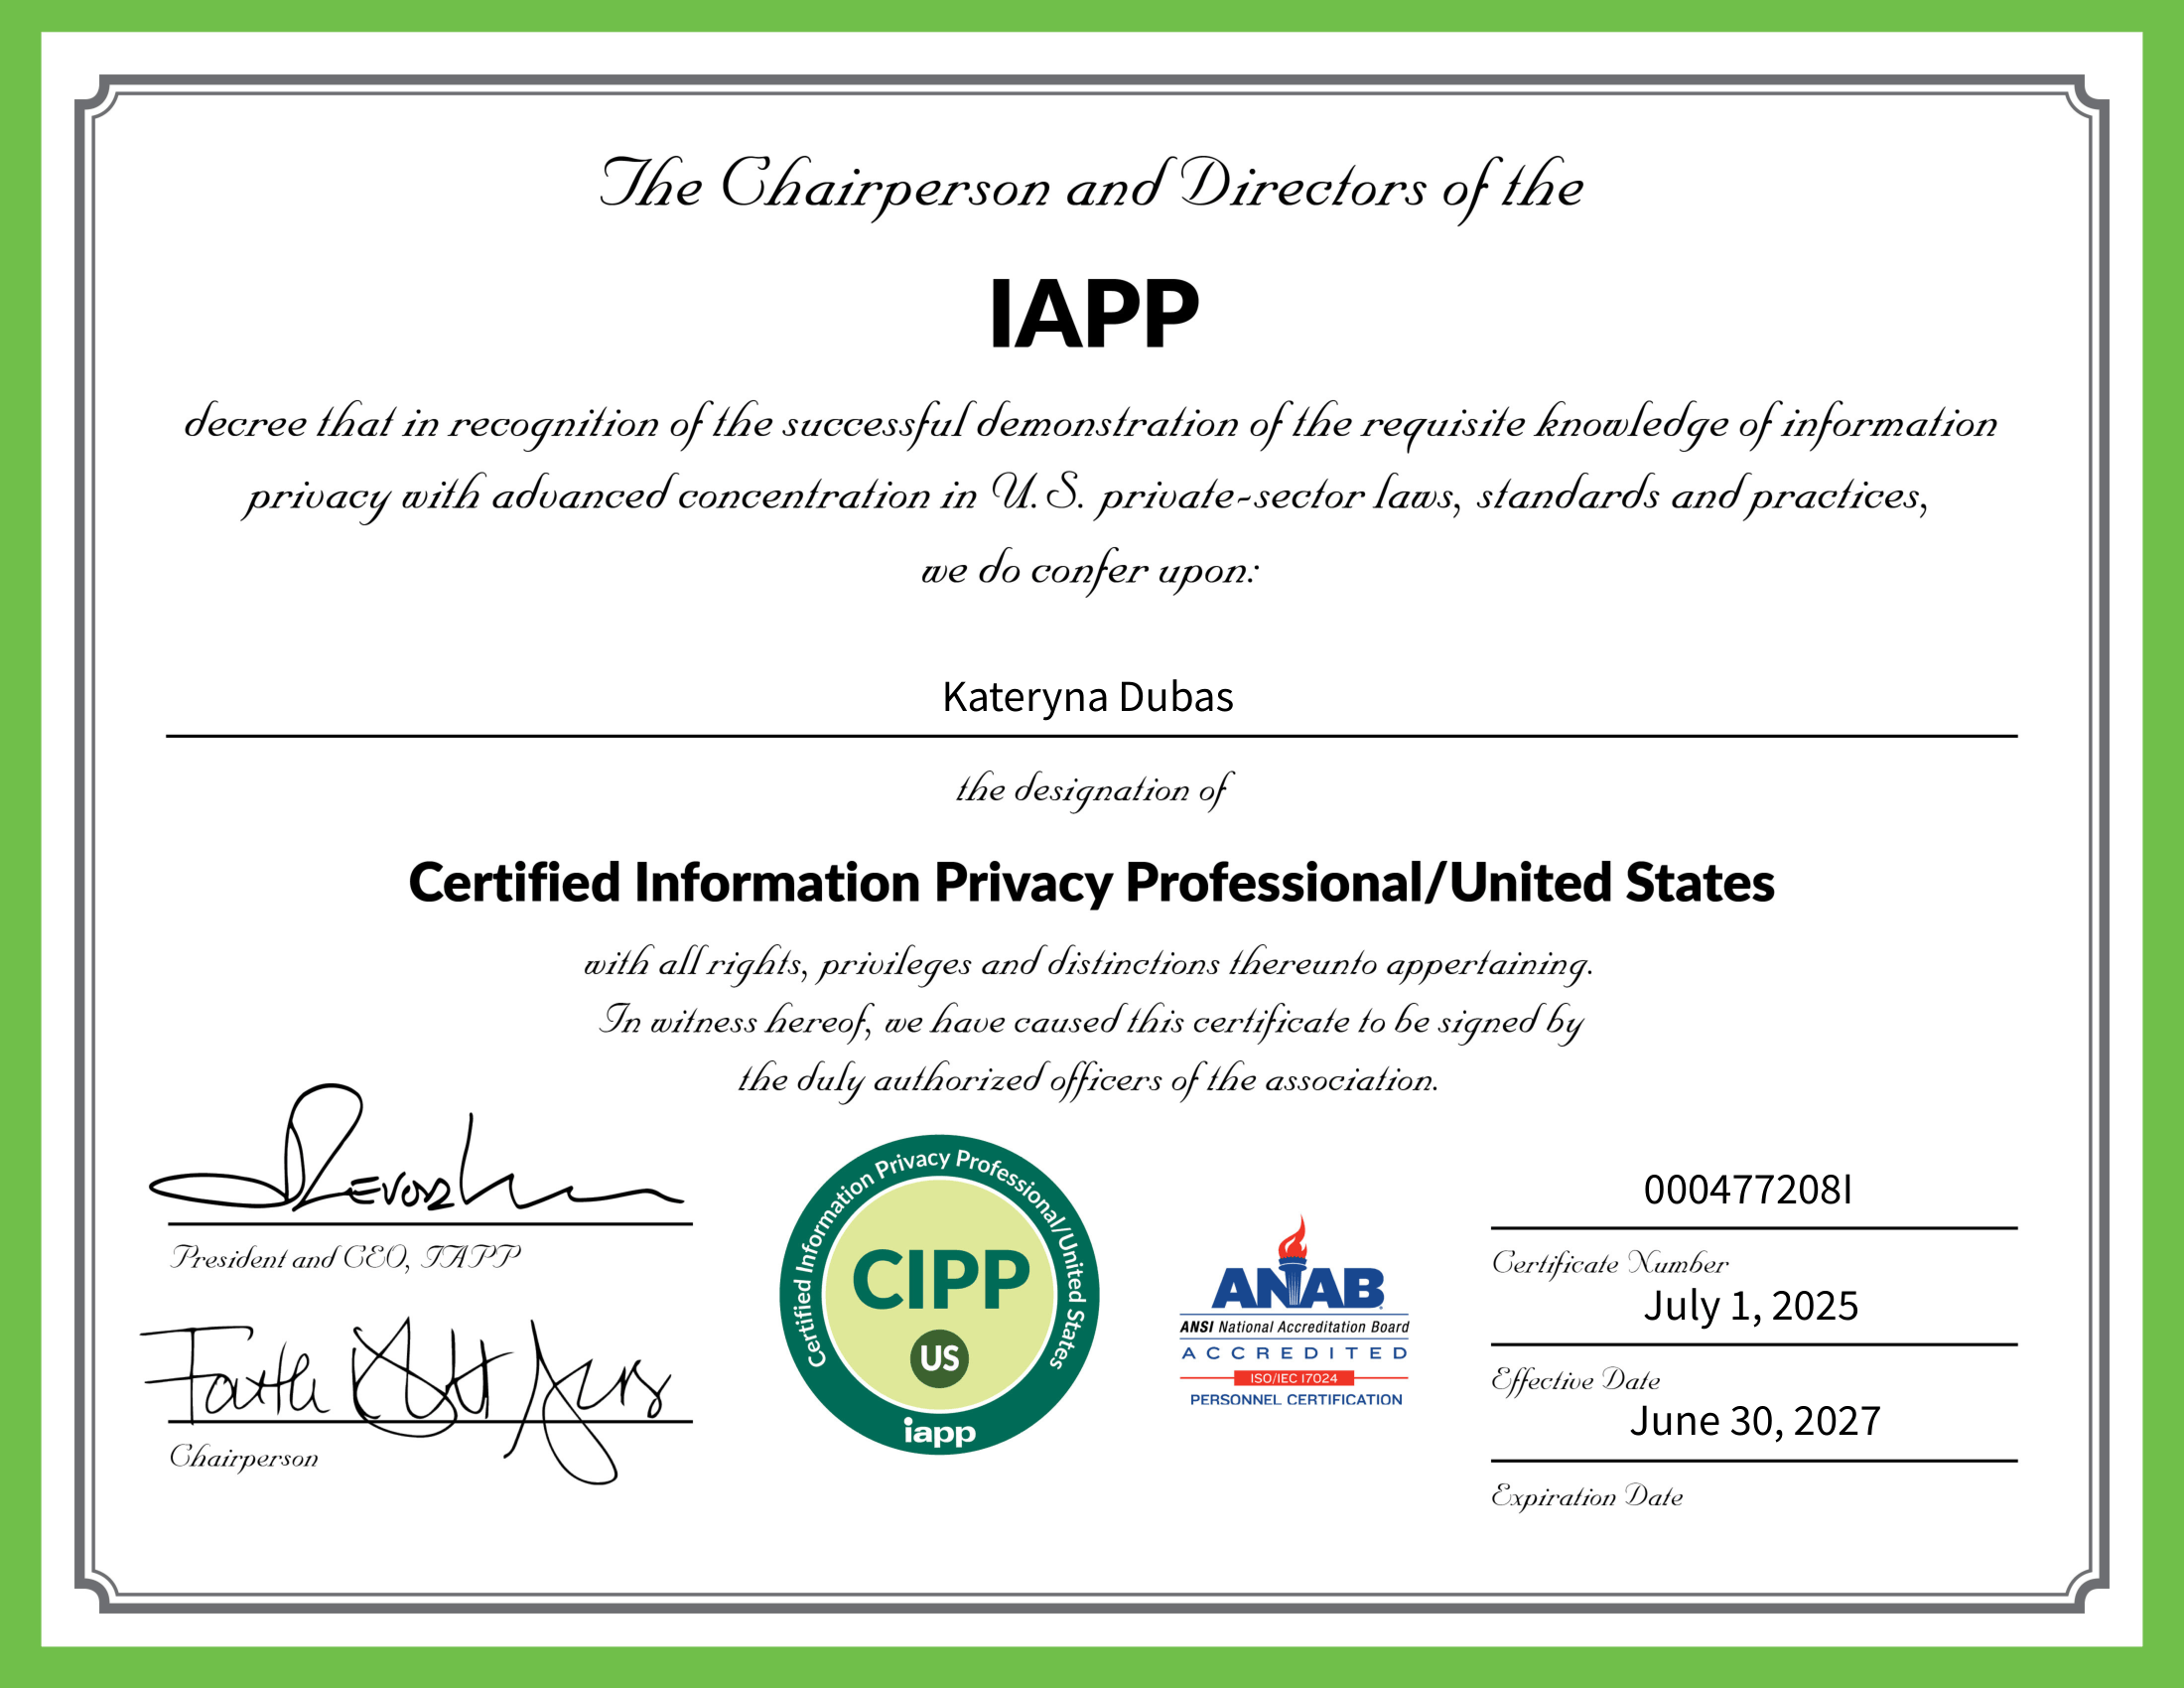
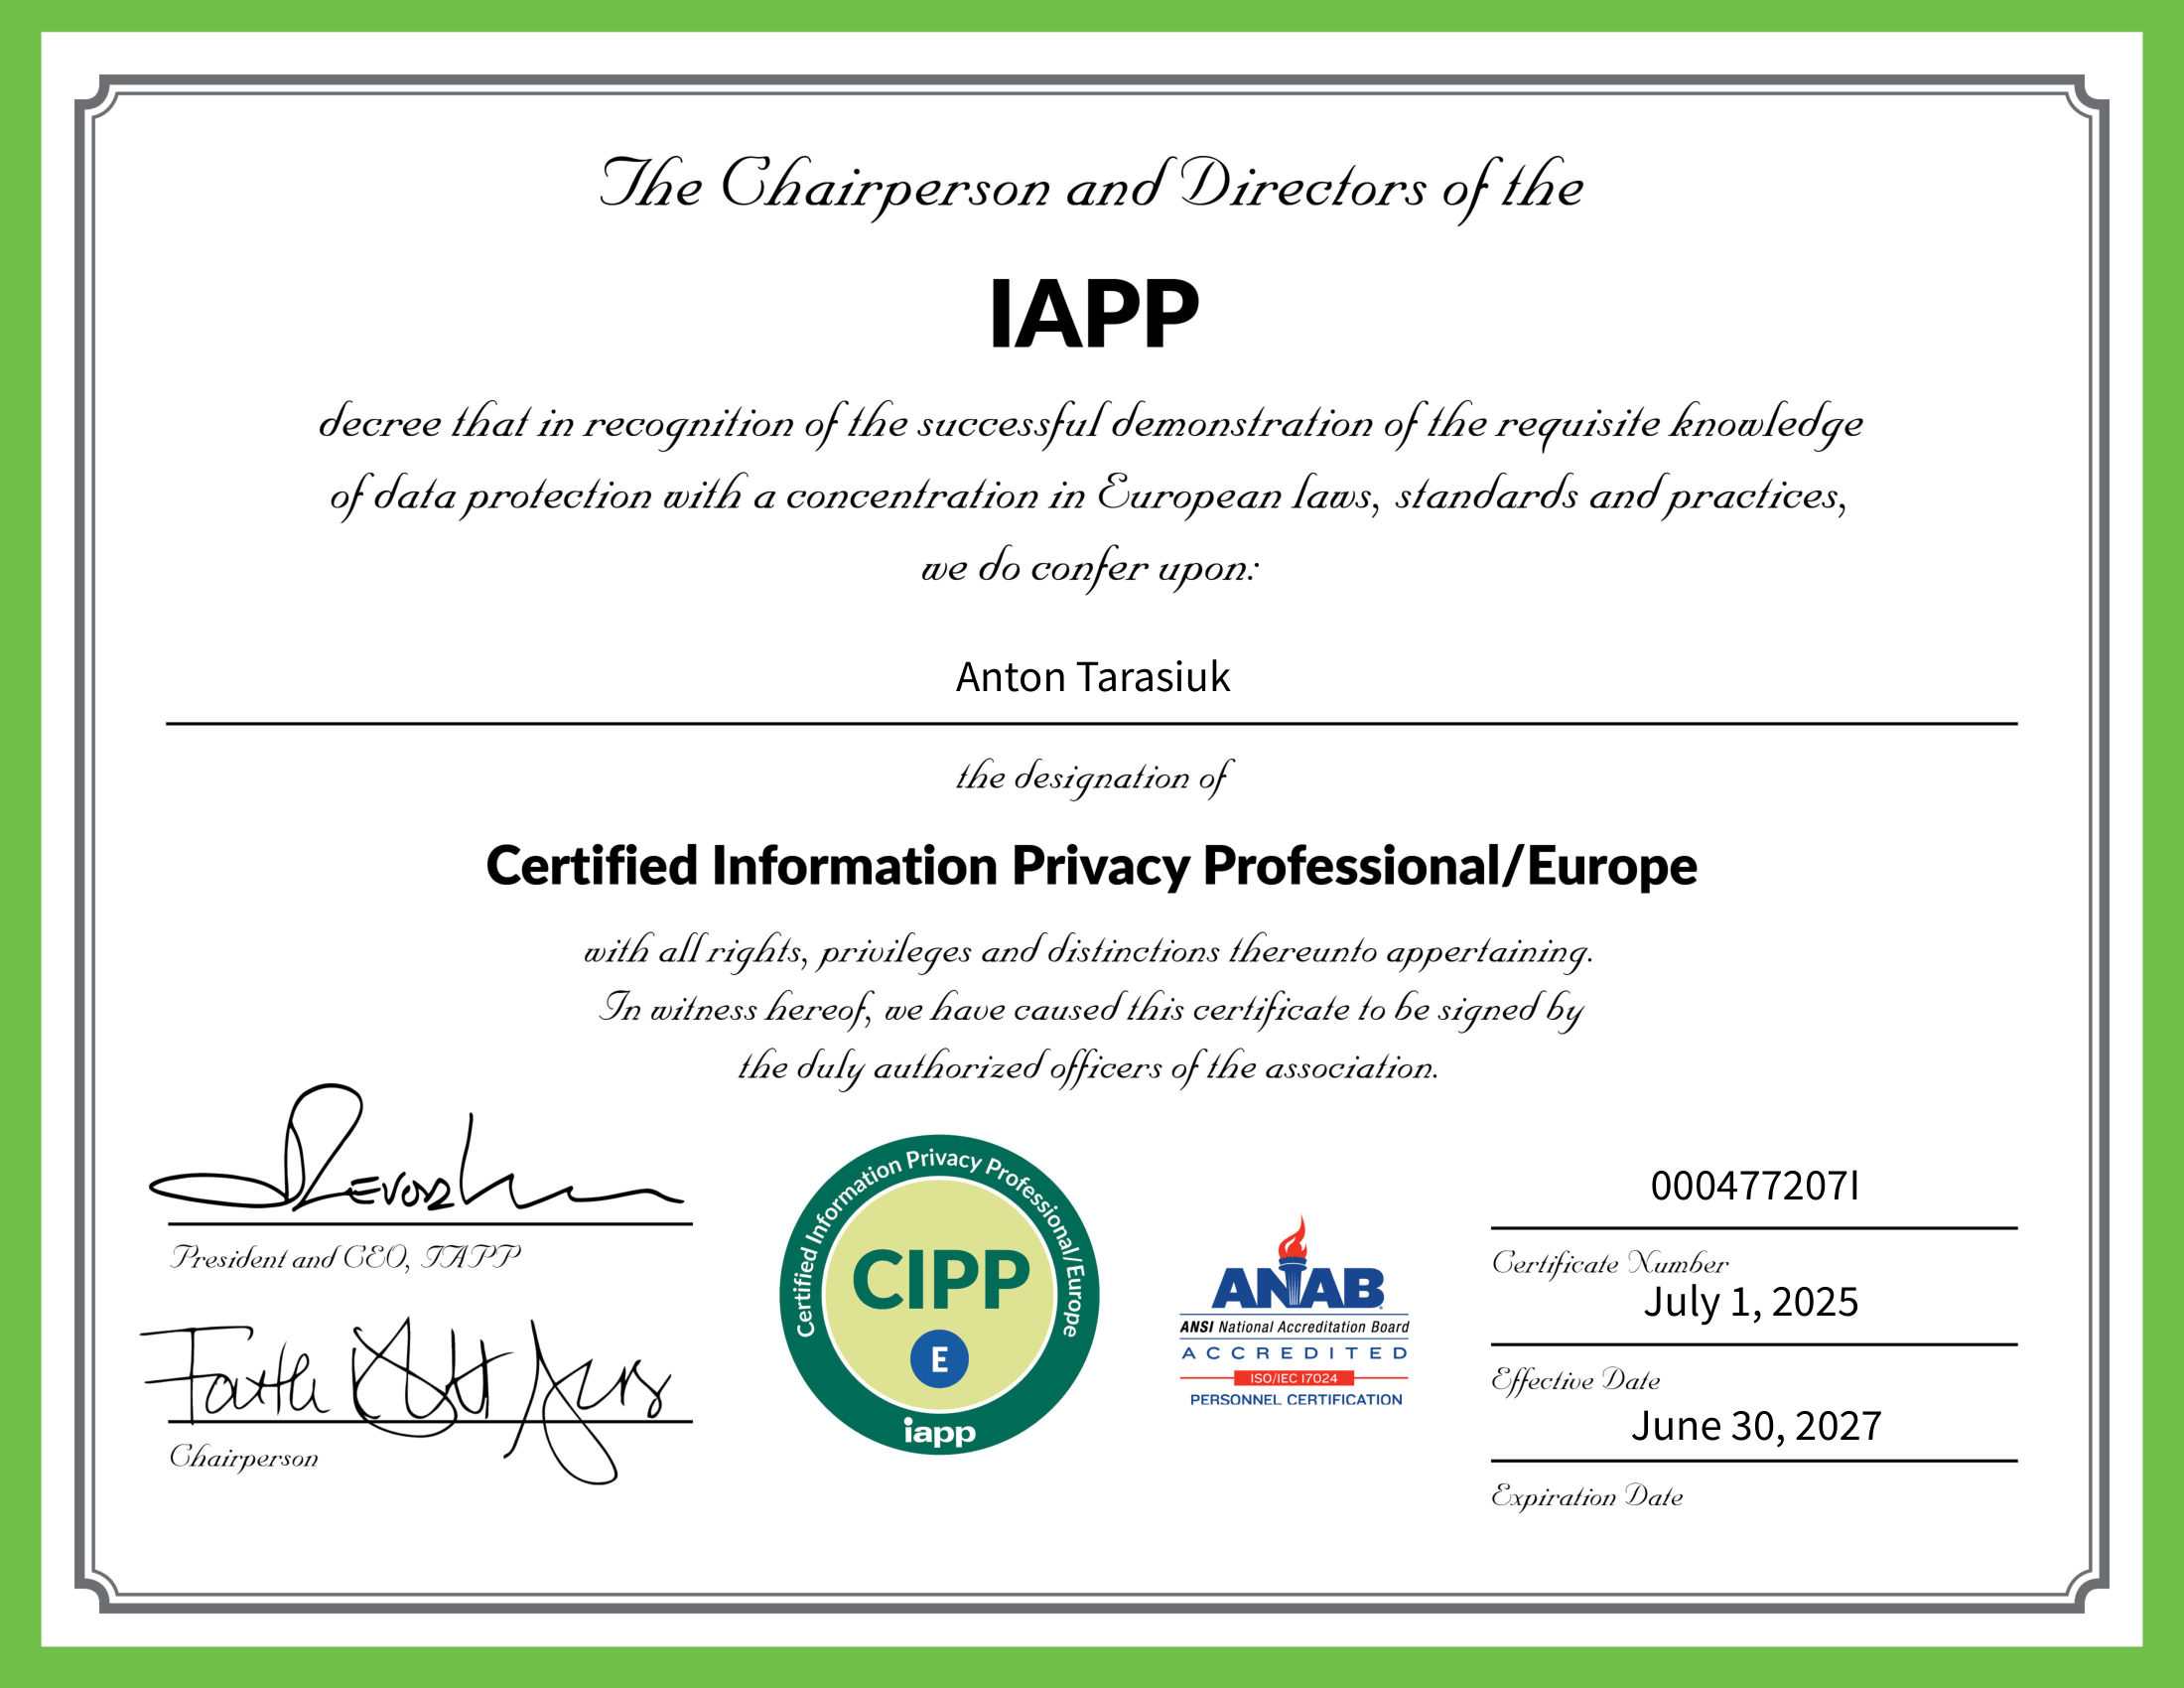
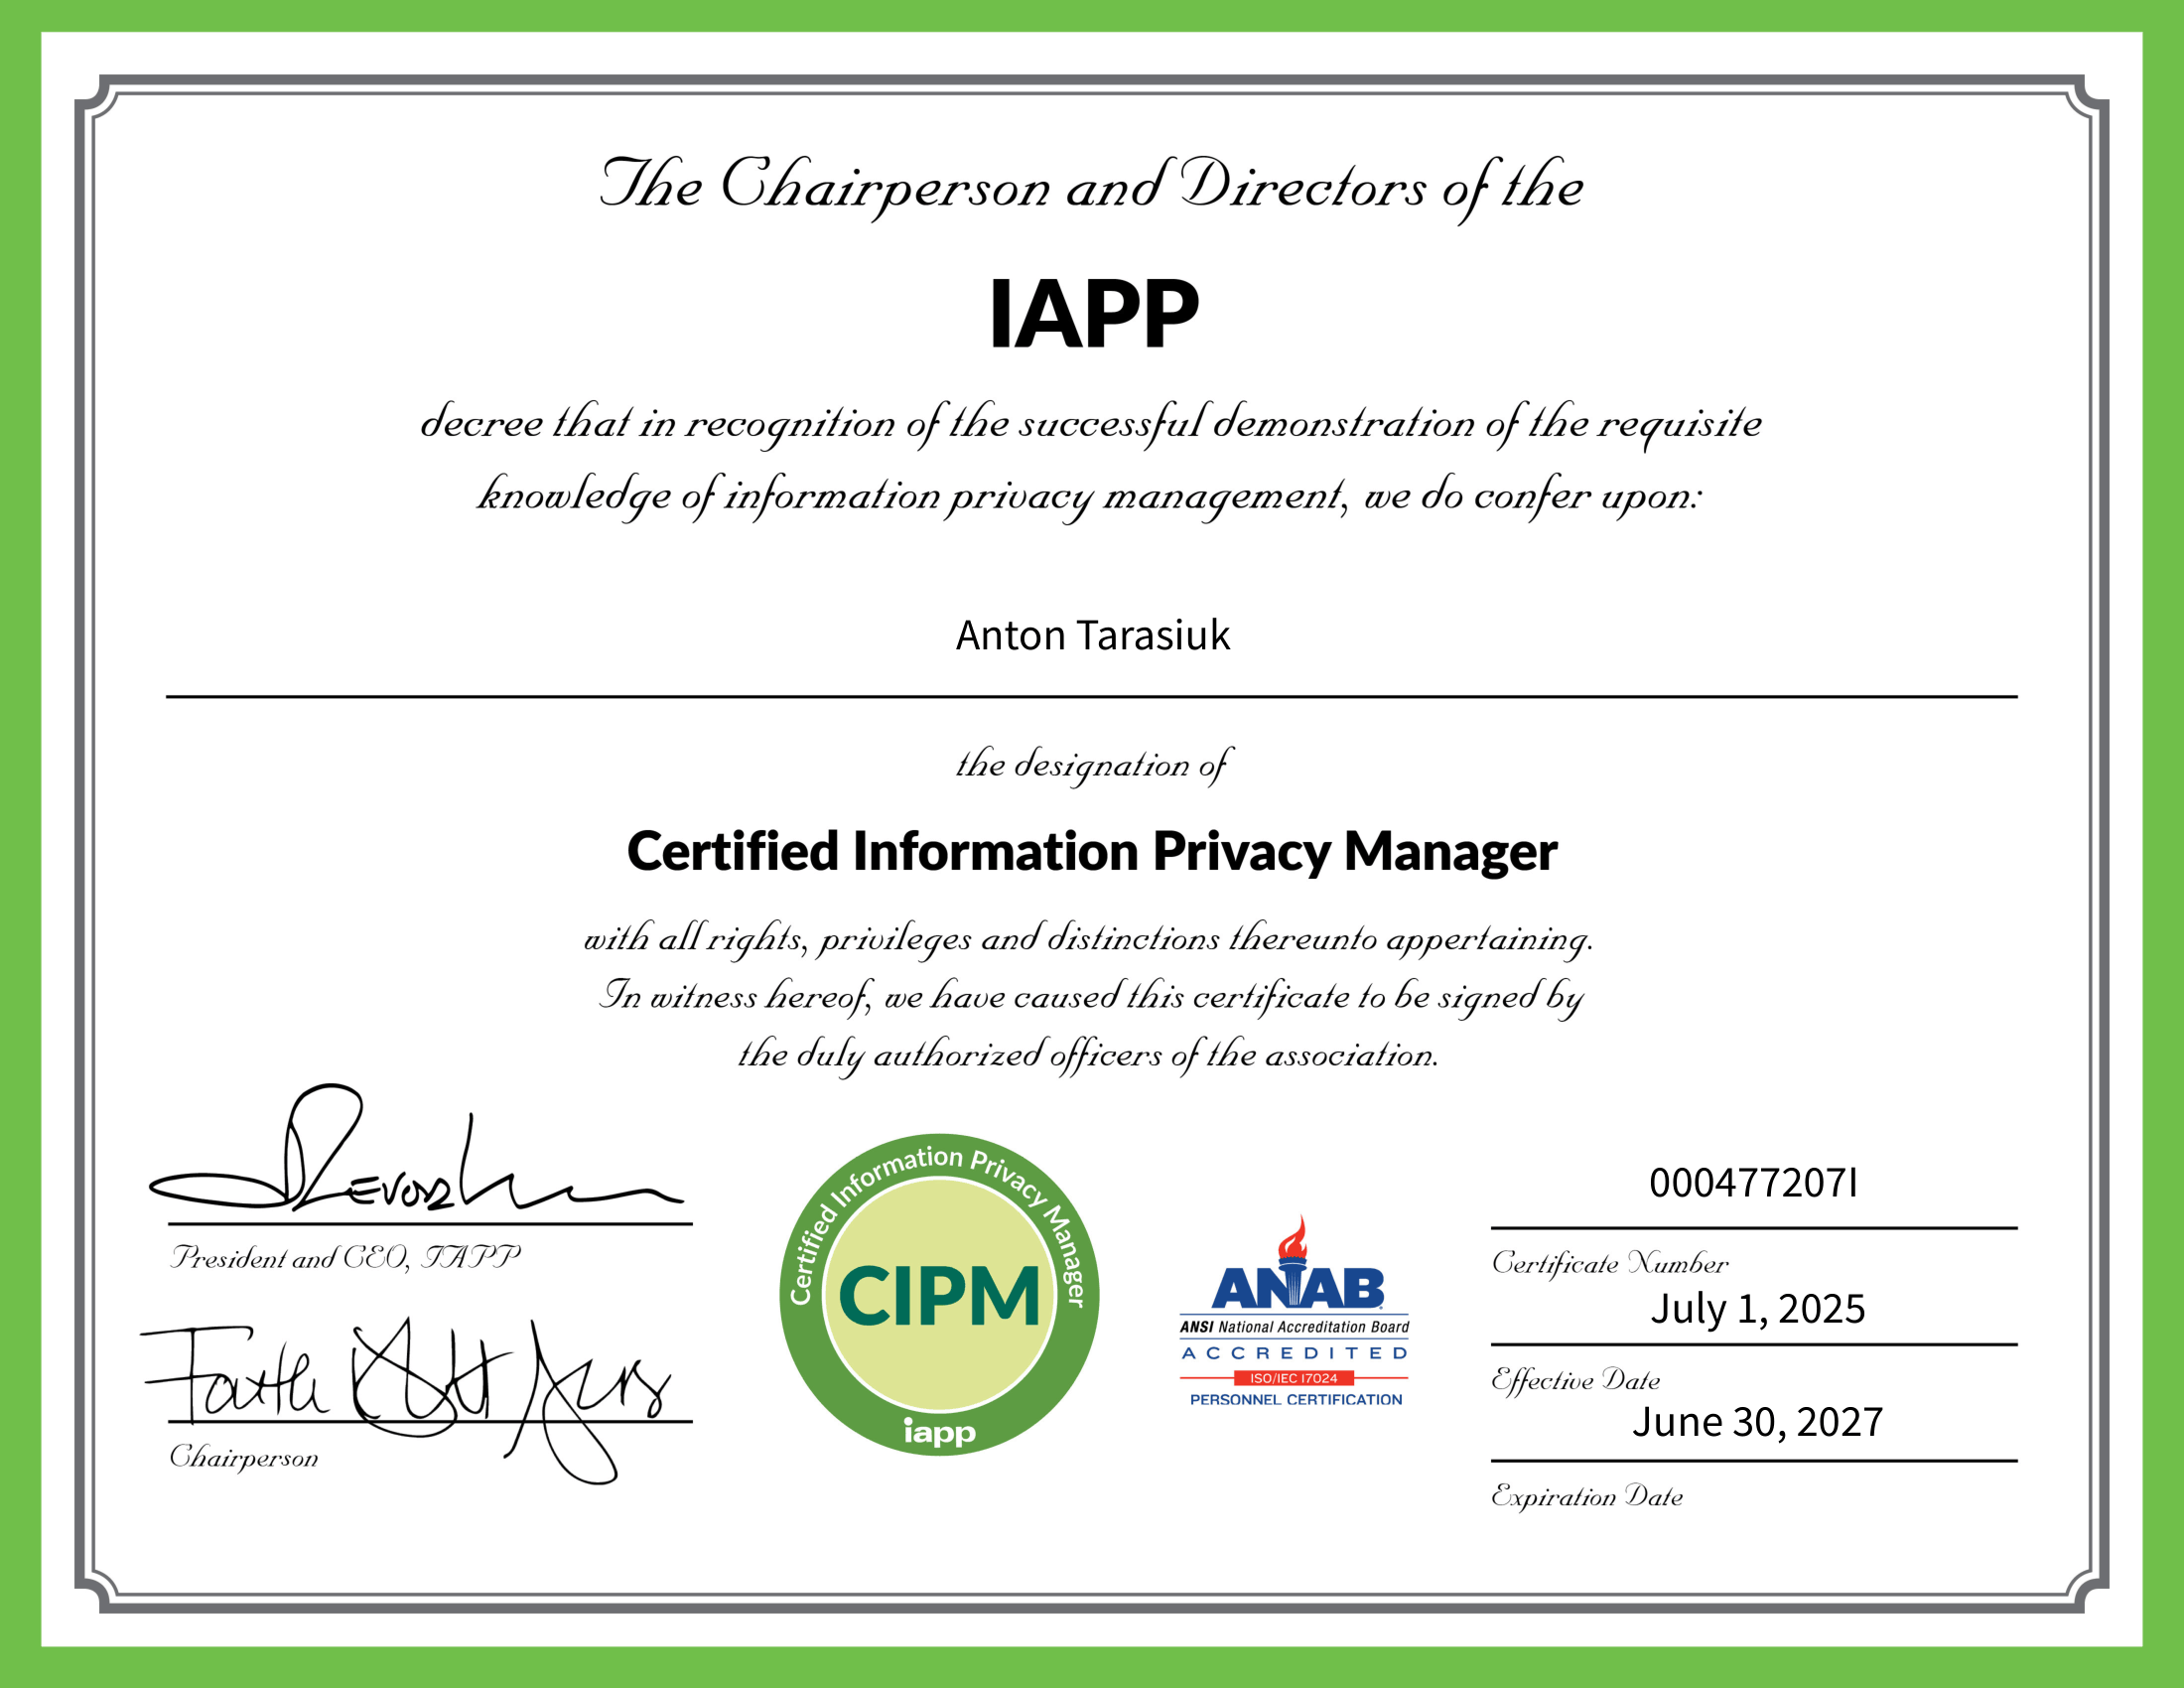
Certified privacy professionals: CISSP, CIPP/E, CIPP/US, CIPM, CIPT, FIP.





 Relevant and Practical Articles
To protect copyrights in IT, it is important to record your authorship (date of creation, registration with Ukrpatent), enter into agreements with clear terms, use product licenses, sign NDAs with partners, and implement digital watermarks or signatures in products. If your rights are violated, contact legal experts, such as Legal IT, who can help you monitor violations and take legal action to protect your intellectual property.
To protect your copyright in IT, it is important to record your authorship (date of creation, registration with Ukrpatent), enter into contracts with clear terms, use product licenses, sign NDAs with partners, and implement digital watermarks or signatures in products. If your rights are violated, contact legal experts, such as Legal IT, who can help you monitor violations and take legal action to protect your intellectual property.
To protect copyrights in IT, it is important to record your authorship (date of creation, registration with Ukrpatent), enter into contracts with clear terms, use product licenses, sign NDAs with partners, and implement digital watermarks or signatures in products. If your rights are violated, contact legal experts, such as Legal IT, who can help you monitor violations and take legal action to protect your intellectual property.
To protect copyrights in IT, it is important to record your authorship (date of creation, registration with Ukrpatent), enter into contracts with clear terms, use product licenses, sign NDAs with partners, and implement digital watermarks or signatures in products. If your rights are violated, contact legal experts, such as Legal IT, who can help you monitor violations and take legal action to protect your intellectual property.
Legal IT Group provides GDPR (EU) and CCPA (California) compliance services with the support of a professional team holding CIPP/E, CIPP/US, CIPM, CIPT, LLM, and FIPP certifications. The firm helps conduct GDPR audits, draft GDPR documentation (such as Privacy Policy, RoPA, DPA, TIA, LIA, DPIA, etc.), respond to Data Subject Requests, and deliver GDPR training sessions for your team. Legal IT Group also acts as an external DPO for international companies processing millions of users’ data.
Legal IT Group supports companies on matters of cybersecurity, regulatory compliance, and cyber risk management. It assists with implementing the requirements of NIS2, DORA, the Cyber Resilience Act (CRA), GDPR, HIPAA, and other international information security standards. Legal IT Group conducts cybersecurity audits and gap assessments, develops cybersecurity policies and procedures, supports incident response and data breach handling, and advises on risk management, business continuity, supply chain security, and regulatory engagement. Legal IT Group also delivers training for management and staff, and helps product and technology companies achieve compliance with the requirements for operating in the EU market.
The Legal IT Group team works with both startups and large companies, including:
Aurora Multimarket — one of the largest Ukrainian one-dollar-store retail chains.
YouControl — a Ukrainian analytics platform for counterparty verification, company analysis, court records, sanctions lists, and corporate ownership structures.
Nova Poshta — Ukraine’s largest private logistics company, providing delivery services within Ukraine and internationally.
MacPaw — a Ukrainian product IT company known for developing software for macOS and iOS.
UKR.NET — one of Ukraine’s largest internet companies, operating an email service, news portal, and other digital services.
Readdle — an international product IT company of Ukrainian origin, developer of popular mobile applications.
ZONE3000 — a major Ukrainian IT company providing software development, technical support, and digital product services to international clients.
Yuriia-Farm — one of Ukraine’s leading pharmaceutical companies, represented in numerous international markets.
Snov.io — a Ukrainian SaaS platform for sales automation, prospect contact discovery, email marketing, and lead management.
Legal IT Group’s fees depend on the complexity of the project, the scope of work, and the specialists involved. The base hourly rate starts from €120 per billable hour of attorney work. Where a project is personally handled by the practice head or managing partner, the rate is €200 per billable hour.